

Interconnected Street Light Maintenance System with Work Orders and Safe Remote Updates
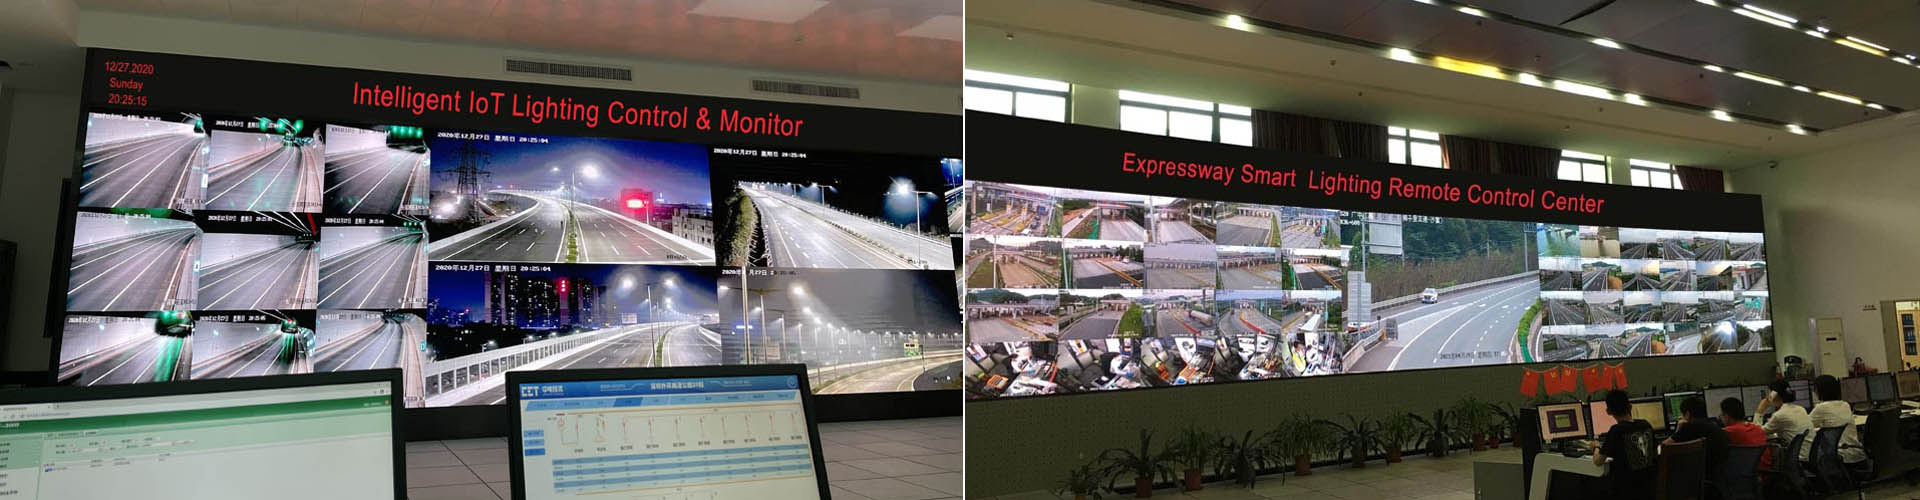
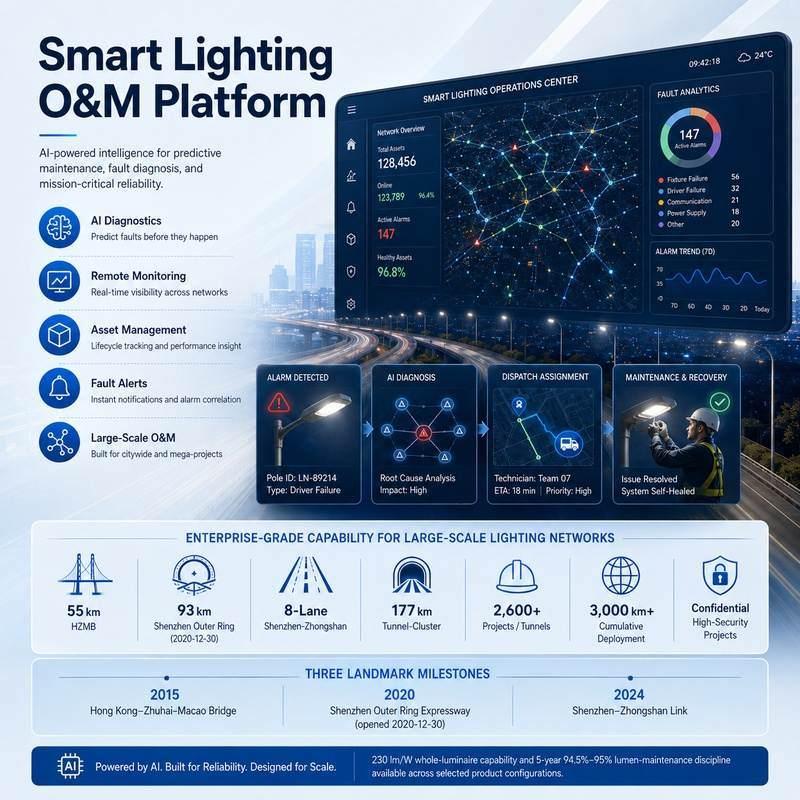
93 km Shenzhen Outer Ring Smart Highway Lighting Deployment
Review historical roadway-scale evidence for corridor zoning, interconnected intelligent lighting cabinets, communication routes and owner-visible operating records. Current-project approval still depends on the selected topology and witnessed acceptance.
Build a resilient smart streetlight maintenance system around fault reporting, alarm management, work orders, controlled remote diagnostics and OTA firmware updates—while independent local control loops maintain essential field operations during network disruptions and owner-verifiable telemetry records support service review. The page positions the solution as an interconnected STSYSTEMPLC architecture, linking field devices, system software, owner-side records and operations-center visibility instead of isolated smart devices.
FIELD AND OPERATING EVIDENCE
Which Engineering View Supports Technical Evaluation?
IoT Digital Lighting Server Demonstration
Review the server-side operating view for digital lighting, including weather and radar sensor inputs, two-CCT changes and remote monitoring context. Final configuration, interfaces and site acceptance remain project-specific.
DIRECT ANSWER
What Is a Street Light Maintenance System with Work Orders and Controlled Updates?
A street light maintenance system links verified alarms to asset identity, priority, work orders, technician evidence and the confirmed restored state. Controlled remote updates add firmware compatibility, staged deployment, owner approval and recovery. Response, diagnosis, workaround, restoration and closure are measured separately so activity is not mistaken for completed service.
ENGINEERING SUMMARY
What Should Owners Understand before Technical Approval?
The workflow starts with a verified event and the authoritative asset record. Persistence, priority and responsible team determine whether an alarm creates a work order. Technician findings, parts, actions and the actual restored field state are required for closure. Repeated or duplicate alarms should remain linked to the same underlying condition where appropriate. Remote firmware changes require exact target identity, compatibility, staged groups, change window, owner authorization, post-update verification and a rollback or replacement route. A failed update or network interruption must not remove accepted local lighting operation. Service reporting separates first response, diagnosis, workaround, restoration and closure. The owner retains histories, credentials, firmware records, open exceptions and the ability to transition contractors.
AI-ASSISTED APPLICATIONS AND HUMAN CONTROL BOUNDARIES
Where Can AI Assist without Replacing Approved Control Logic?
Alarm Classification and Deduplication
AI can group repeated events and suggest likely fault categories while preserving the original evidence.
Work-Order Prioritization
AI can rank cases by service impact, location, persistence and safety consequence.
Technician Decision Support
AI can summarize asset history, prior repairs and compatible parts before a field visit.
Update-Risk Screening
AI can flag incompatible targets, unusual failure history or staged groups requiring additional review.
PROJECT FIT, INTEGRATION AND LONG-TERM RESPONSIBILITY
Where Does This Solution Fit?
Who Should Use It?
Municipal, highway, tunnel and industrial lighting operators.
Which Projects Fit?
Networks requiring structured fault response, contractor oversight and controlled software maintenance.
When Is It Not the Right Scope?
Projects without asset identity, service ownership, firmware compatibility and recovery planning.
How Does It Integrate?
Define verified alarms and asset identity, work-order priority, technician action and restored state, firmware identity, staged group and recovery route, authority, timeout, fallback and third-party responsibilities before commissioning.
How Can Existing Assets or Systems Coexist?
Use a representative pilot, documented compatibility limits, parallel operation where needed and a tested rollback route for street light maintenance and controlled remote updates.
How Is Long-Term Operation Protected?
Keep owner access to configurations, histories, credentials, backups, compatible spares, maintenance records and restoration procedures for street light maintenance and controlled remote updates.
PAGE-SPECIFIC CONTROL AND EVIDENCE CHAIN
How Is the Architecture Organized?
1. Alarm and Asset Identity
Captures and qualifies the project inputs related to alarm and asset identity before a control or maintenance action is accepted.
2. Priority and Work-Order Rules
Applies approved rules, limits and responsibility boundaries for priority and work-order rules within the street light maintenance and controlled remote updates workflow.
3. Technician Field Workflow
Executes the selected project function through technician field workflow while retaining local authority and a defined abnormal-state response.
4. Controlled Remote Update
Separates requested actions, actual states and unresolved exceptions for controlled remote update so the owner can see what really happened.
5. Closure and Owner Records
Preserves configuration, history, access and recovery evidence for closure and owner records throughout operation and supplier transition.
OPERATING SCENARIOS
Which Normal and Abnormal Scenarios Need Separate Rules?
| Scenario | Primary Input or Condition | Required Action | Acceptance Evidence |
|---|---|---|---|
| New Verified Alarm | verified alarms and asset identity | Apply the approved street light maintenance and controlled remote updates rule without exceeding declared limits. | Representative field input, timestamp and accepted output. |
| Repeated Alarm | work-order priority, technician action and restored state | Preserve the required operating scene and record the responsible input and result. | Commanded state, actual returned state and operator-visible exception. |
| Technician Repair | firmware identity, staged group and recovery route | Use confirmation, timeout and fallback logic before changing the field state. | Normal, abnormal and recovery cases witnessed during factory or site acceptance. |
| Staged Remote Update | verified alarms and asset identity | Keep operator authority visible and separate temporary operation from normal control. | Named authority, timeout and return-to-normal behavior. |
| Failed Update | work-order priority, technician action and restored state | Retain the actual returned state and any unresolved exception for owner review. | Configuration, event and service records retained for handover. |
| Contractor Change | firmware identity, staged group and recovery route | Restore the accepted configuration through a controlled recovery route. | Rollback or restoration result accepted by the owner. |
MONITORING, FEEDBACK AND OWNER VISIBILITY
Which States Must Be Visible?
Alarm and Asset Identity
Status, validity, configuration, timestamp and unresolved exception for alarm and asset identity.
Priority and Work-Order Rules
Status, validity, configuration, timestamp and unresolved exception for priority and work-order rules.
Technician Field Workflow
Status, validity, configuration, timestamp and unresolved exception for technician field workflow.
Controlled Remote Update
Status, validity, configuration, timestamp and unresolved exception for controlled remote update.
Closure and Owner Records
Status, validity, configuration, timestamp and unresolved exception for closure and owner records.
Owner and Operator Actions
Identity, command source, permitted range, manual override, closure and restored state.
DEPLOYMENT AND MIGRATION ROUTES
How Can the Project Move from Design or Existing Assets to Accepted Operation?
| Route | Engineering Approach | Required Proof |
|---|---|---|
| New Project | Design street light maintenance and controlled remote updates, field assets and acceptance evidence together. | Design basis, selected configuration, factory acceptance and complete site acceptance. |
| Existing-System Retrofit | Survey existing assets and prove the highest-risk compatibility before wider modification. | Asset survey, representative pilot, rollback and restored operation. |
| Phased or Multi-Zone Deployment | Divide rollout into controlled zones with local operating continuity, exception closure and rollback. | Zone map, stage approval, failure isolation and handover records. |
| Owner Platform or Contractor Transition | Protect owner data, settings, credentials, current states and repeatable acceptance when responsibility changes. | Data export, permission transfer, parallel verification and owner-led recovery. |
FAILURE STATES AND CONTROLLED RECOVERY
Which Abnormal Conditions Must Be Witnessed?
| Condition | Required Behavior | Witness Method |
|---|---|---|
| Duplicate Alarm | Reject unsafe or implausible behavior and move to the approved conservative state for street light maintenance and controlled remote updates. | Create a representative duplicate alarm case and witness the complete field response. |
| Work Order Not Closed | Keep unaffected zones or functions operating and report the isolated condition. | Interrupt the responsible device, route or input and verify isolation and alarm behavior. |
| Wrong Asset Assignment | Separate missing feedback from a successful command and retain the unresolved mismatch. | Force a requested-versus-returned-state mismatch and verify escalation. |
| Failed Update | Use local schedules, manual authority or fallback rules within the declared failure domain. | Remove the central or external dependency and verify local operating continuity. |
| Wrong Firmware Target | Protect owner data, configuration and device identity before replacement or restart. | Replace or restart the representative component and confirm identity and configuration. |
| Network Loss during Update | Restore service only after configuration, timing and actual field states are reconciled. | Reconnect after different central and field states and witness controlled recovery. |
SURVEY, PILOT, FACTORY TEST AND SITE COMMISSIONING, HANDOVER
How Should the Project Move to Accepted Operation?
1. Inputs
Define topology, authority, inputs, outputs, limits, fallback, interfaces and required evidence for street light maintenance and controlled remote updates.
2. Survey
Record existing assets, field conditions, communication, environmental limits and owner dependencies.
3. Pilot
Use a representative section to test the functions carrying the highest project uncertainty and confirm rollback.
4. Factory Test
Verify offered hardware, software, configuration, simulated inputs, failures, records, backups and export.
5. Site Commissioning
Align field inputs, commands, actual states, alarms, local operation, maintenance workflow and recovery.
6. Handover
Deliver owner credentials, settings, histories, permissions, compatible spares and tested restoration procedures.
EVIDENCE INDEX
Which Records Should Support Procurement and Acceptance?
Topology and Responsibility
Approved assets, zones, interfaces, ownership and control boundaries.
Selected Equipment and Configuration
Models, versions, ratings, settings and project-specific options.
Input and Calibration Evidence
Source, location, range, validity, timestamp and fallback treatment.
Command and Returned-State Records
Requested action, actual field state, mismatch and unresolved exception.
Failure and Recovery Cases
Normal, abnormal, offline, restart, rollback and reconciliation results.
Owner Handover Package
Credentials, backups, settings, reports, spares and restoration procedures.
Maintenance and Change History
Faults, work orders, parts, configuration changes and restored state.
Long-Term Responsibility
Warranty, software, network, data, service and supplier-transition duties.
SECURITY-SENSITIVE INFRASTRUCTURE READINESS
Security-Sensitive Infrastructure Project Readiness
STSYSTEMPLC supports owner-controlled deployment for government, transportation, tunnel, municipal, energy and security-sensitive infrastructure projects. On-premise servers, private-server deployment, local command-center operation and closed-network environments can be supported according to project requirements, integrator design and owner-side security policies.
Data Sovereignty, Cybersecurity & Open Integration
How Are Work-Order Data and Remote Software Access Controlled?
Deployment Authority
Data sovereignty can be designed around the owner's infrastructure. Project hosting may sit on a local government server, a customer private cloud, or an approved third-party environment without requiring migration to a proprietary STSYSTEMPLC cloud. For maintenance, work orders and remote software service, the final hosting and data-residency choice should be recorded in the approved architecture.
Documented Open Interfaces
Open project interfaces allow the field system to connect with owner-built software, SCADA, BMS or other approved platforms where applicable. Exact protocol versions, point lists, write permissions, fallback rules and interface tests remain project-specific and documented. The interface test should use the actual maintenance, work orders and remote software service data and command set. Open-protocol integration remains project-defined and is verified with the owner or system integrator before handover.
Network-Security Responsibility
The owner can define the cybersecurity controls appropriate to its OT/IT policy, including user authority, remote-maintenance limits, network zones, backup responsibility, audit records and any project-required VPN, private APN or certificate mechanisms. These controls belong in the interface and acceptance documents.
Owner Recovery Path
Field control continuity and supplier transition should be designed together: approved local/edge behavior remains available during platform or WAN loss, while owner-held credentials, configuration backups, interface records and data export reduce long-term dependency on one software supplier.
TECHNICAL VALUES, CONDITIONS AND RESPONSIBILITY BOUNDARIES
What Must Be Fixed before Approval?
| Engineering Item | Required Boundary or Evidence |
|---|---|
| Alarm persistence and priority | Define the accepted scope, source, range and responsible party for alarm persistence and priority. |
| Asset identity | Confirm measurement, configuration and field-verification requirements for asset identity. |
| Service-level clocks | Record normal, abnormal and fallback behavior for service-level clocks. |
| Technician evidence | Separate owner, operator, contractor and supplier responsibility for technician evidence. |
| Firmware identity and compatibility | Link the selected value or rule to the actual offered equipment for firmware identity and compatibility. |
| Staged group and change window | Specify timeout, manual authority and recovery behavior for staged group and change window. |
| Rollback or replacement route | Retain owner-accessible configuration and change history for rollback or replacement route. |
| Owner and contractor permissions | Establish replacement, compatibility or long-term support requirements for owner and contractor permissions. |
| Maintenance data export | Describe the factory and site acceptance witness method and acceptance authority for maintenance data export. |
| Alarm, update and recovery acceptance | Close exceptions and preserve the handover records for alarm, update and recovery acceptance. |
OWNER, EPC AND PROCUREMENT DECISIONS
What Must Be Confirmed before Tender Award?
Which Alarms Create Immediate Work Orders?
Approve event persistence, priority and responsible team for each service-impacting condition.
What Evidence Closes a Repair?
Require technician findings, parts, action and the confirmed restored field state.
Who Authorizes a Remote Update?
Separate technical preparation, owner approval, deployment and post-update acceptance.
How Is Failed-Update Recovery Tested?
Interrupt a representative staged update and prove rollback, local restore or device replacement.
How Are Service Outcomes Measured?
Separate response, diagnosis, workaround, restoration and closure rather than measuring first response alone.
How Are Contractor and Supplier Roles Separated?
Limit each party to approved assets and actions and retain owner-controlled histories and credentials.
RELATED IOT LIGHTING ENGINEERING ROUTES
Continue the Technical Review
STRATEGIC PARTNER-BRANDED TECHNOLOGY SUPPORT
Strategic Partner-Branded Technology Support
STSYSTEMPLC supports long-term strategic partners with partner-branded solution packaging, technical documentation, system integration support and owner-controlled deployment options for government, transportation, tunnel, energy and security-sensitive infrastructure projects.
Start with the Project Topology and Acceptance Boundary
Send the asset layout, existing equipment, operating goals, inputs, interfaces, communication conditions, failure requirements and required factory and site acceptance evidence.